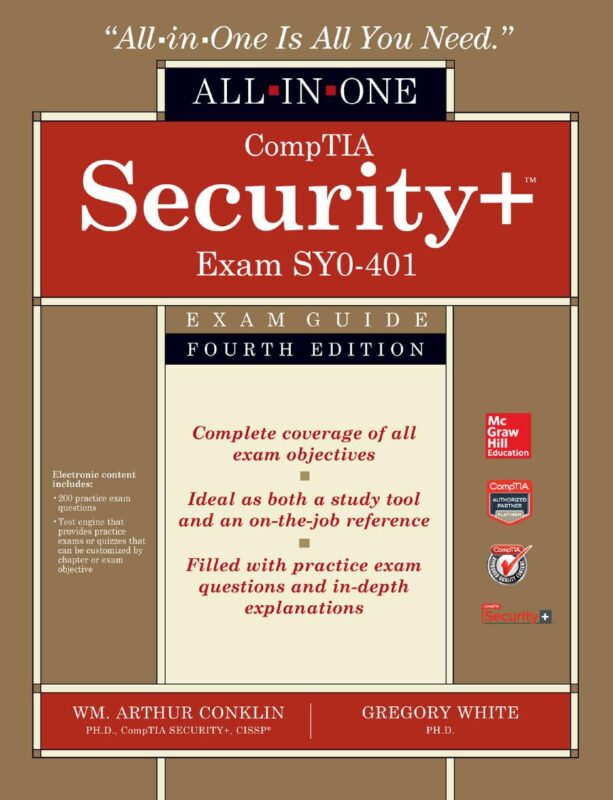
CompTIA Security+ All-in-One Exam Guide, (Exam SY0-401) 4th Edition By Arthur Conklin, Greg White, Dwayne Williams, Chuck Cothren, Roger Davis
$25.00
Secure checkout
Instant digital download
PDF document
Document details
- Pages
- 607
- File size
- 21.02 MB
- Format
- Digital PDF
- Category
- eBook[PDF]
Sign in or create a free account to continue. Your purchase will be saved in My Downloads.
About this ebook
The CompTIA Security+ All-in-One Exam Guide, 4th Edition by Wm. Arthur Conklin and Greg White completely mirrors the official objectives of the CompTIA Security+ SY0-401 exam. [1]
1. Network Security (20% of the exam)
- Network Devices: Deploying and configuring routers, firewalls, switches, load balancers, proxies, and web security gateways.
- Network Administration: Implementation of firewall rules, Access Control Lists (ACLs), VLAN management, and port security.
- Secure Protocols: Working with foundational secure protocols such as SSH, TLS/SSL, HTTPS, IPsec, and SFTP.
- Wireless Security: Securing wireless connections using WEP, WPA, and WPA2. [1, 2, 3]
2. Compliance and Operational Security (18% of the exam)
- Risk Management: Risk assessment, business impact analysis (BIA), and calculating risk mitigation strategies.
- Policies and Procedures: Implementing acceptable use policies, separation of duties, and onboarding/offboarding practices.
- Incident Response: Best practices for handling security breaches, disaster recovery, and business continuity.
- Physical Security: Controls like locks, badges, CCTV, environmental controls (HVAC, fire suppression), and fencing. [1, 2]
3. Threats and Vulnerabilities (20% of the exam)
- Malware Types: Understanding viruses, worms, Trojans, rootkits, ransomware, and spyware.
- Social Engineering: Analyzing attacks like phishing, vishing, tailgating, and shoulder surfing.
- Attack Types: Identifying network attacks (DDoS, man-in-the-middle, ARP poisoning) and wireless threats (evil twins, rogue access points).
- Vulnerability Assessment: Utilizing vulnerability scanners, conducting penetration testing, and managing risk factors. [1, 2, 3]
4. Application, Data, and Host Security (15% of the exam)
- Application Security: Mitigating web application attacks like SQL injection and Cross-Site Scripting (XSS).
- Host Hardening: Securing operating systems, using anti-malware, host-based firewalls, and managing patches.
- Data Protection: Concepts behind Data Loss Prevention (DLP) and securing data at rest, in transit, and in use. [1, 2, 3]
5. Access Control and Identity Management (15% of the exam)
- Authentication Services: Implementing protocols like RADIUS, TACACS+, and LDAP.
- Identity Management: Implementing Single Sign-On (SSO) and Multi-Factor Authentication (MFA).
- Access Control Models: Understanding MAC (Mandatory), DAC (Discretionary), RBAC (Role-Based), and ABAC (Attribute-Based) controls. [1]
6. Cryptography (12% of the exam)
File included
tmpphpJkj0p8
21.02 MB
Related ebooks